
Threat Intelligence team from Group-IB recently uncovered an ongoing phishing campaign targeting corporate email accounts by exploiting Microsoft file sharing services, including Sway, SharePoint, and OneNote. Codenamed as “PerSwaysion” – the phishing campaign attacked around 156 high ranking officers of various organizations across the U.S, Canada, Germany, the U.K., Netherlands, Hong Kong, Singapore, and several other countries. The group sent phishing emails to top-level executives at targeted companies to trick them into entering Office 365 credentials on fake login pages. Group-IB created a website for users to check if their email address was compromised by PerSwaysion group.
According to Group-IB, PerSwaysion has been active since 2019. It is said that PerSwaysion is a collection of targeted phishing attacks operated by multiple hackers’ groups, attacking small and medium financial services companies, law firms, and real estate groups.
The researchers also stated that the campaign adopts multiple techniques to avoid traffic detection and automated threat intelligence gathering, which include:
- Whitewashing: Using legit file sharing sites as a jumping board; Using web application hosting from reputable vendors such as Google’s AppSpot and IBM’s MyBlueMix
- Counter-intelligence: Randomizing malicious JS file names; Fingerprinting victim browsers and rejecting repeated visits
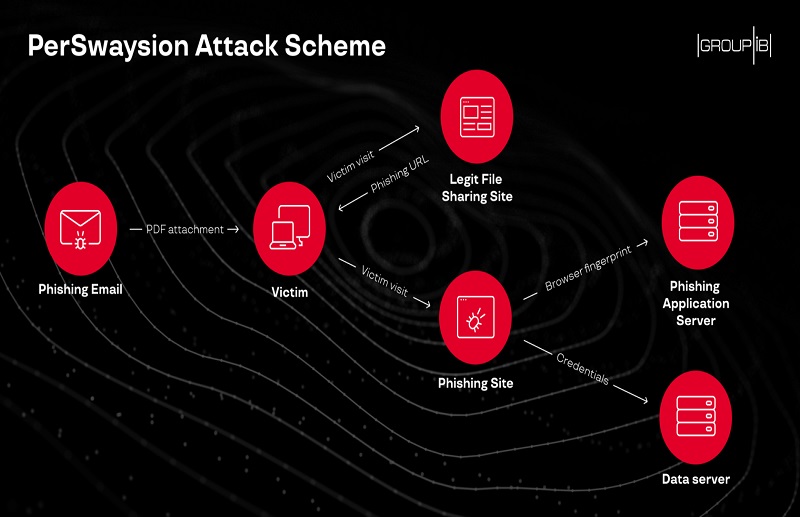
PerSwaysion Attack Methodology
- Attackers send an email containing a clean PDF file as an email attachment to the targeted user. When the user opens the attachment, they’d be asked to click on a link to view the actual content
- The link then redirects the users to a Microsoft Sway (newsletter service) page, where a similar file would ask the victim to click on another link
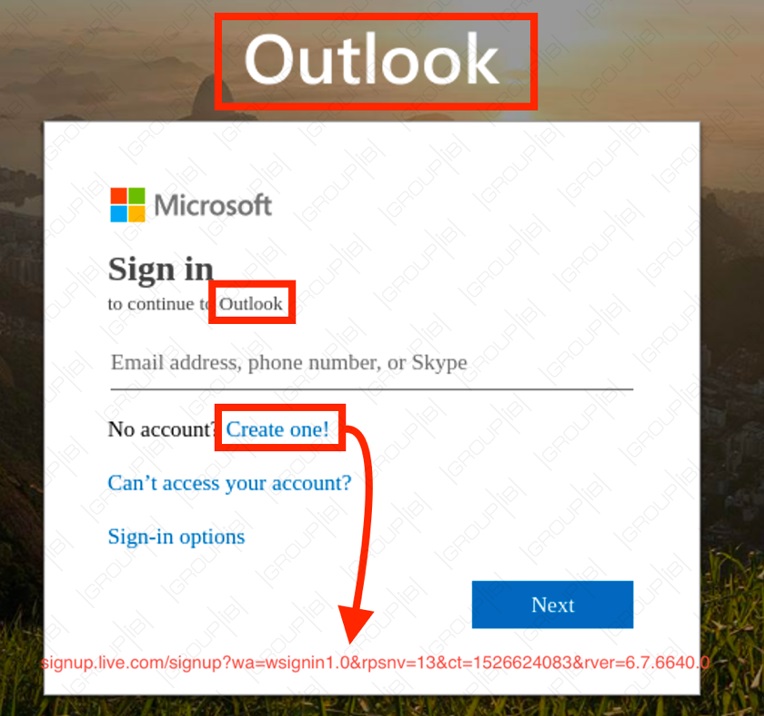
- This will again redirect the user to a page imitating the Microsoft Outlook login page, where hackers would collect the victim’s credentials
Phishing Site Disguised as Microsoft Sign In Page
Describing the PerSwaysion campaign, Feixiang He, Senior Threat Intelligence Analyst at Group-IB, said, “PerSwaysion campaign is a living example of highly specialized phishing threat actors working together to conduct effective attacks on high ranking officers in large scale. They adopt multiple tactics and techniques to avoid traffic detection and automated threat intelligence gathering, such as the use of file-sharing services and web application hosting from reputable vendors.”
“The campaign pursues non-trivial counterintelligence methods, for example, randomizing malicious JS file names and fingerprinting victim browsers and rejecting repeated visits. Such measures taken by cybercriminals seeking to garner sensitive corporate information requires non-standard approach to their detection and response,” He added.

